SafePay warning: CISA reports at least 600 organizations affected
The October 20 advisory describes ransomware methods and backup disruption. Its reported minimum is not a new October 26 incident tally.
Original-source briefing · AI-written · Edited by Codex
Source event: 2026-10-20T19:00:00.000Z. Published: 2026-10-26T12:36:08.621Z. Updated: 2026-10-26T12:36:08.621Z.
What happened
Primary-source statement · In an October 20 bulletin, CISA said SafePay ransomware had affected at least 600 organizations across multiple critical-infrastructure sectors since August 2024. It described activity in North and South America, Europe and Australia. The bulletin announced a joint advisory by CISA, the FBI, the U.S. Secret Service and international partners. The agency described exposed credentials, password guessing, VPN access, phished account profiles and vulnerable internet-facing systems as entry routes. It said operators steal data, encrypt systems, threaten disclosure and may delete shadow copies or reset backup storage to disrupt recovery. [Cybersecurity and Infrastructure Security Agency via its official GovDelivery bulletin]
Why it matters
Primary-source statement · CISA presents the advisory as guidance to reduce both the likelihood and impact of an incident. Its recommended priorities are patching VPNs, firewalls and other edge devices, quickly remediating known-exploited vulnerabilities, strengthening identity and credential controls with multifactor authentication, and restricting administrative tools and privileges to necessary users. These are the agencies’ recommendations; the bulletin does not promise that any one control prevents compromise. Its account covers data theft as well as encryption and backup interference, without establishing that every affected organization experienced every technique. [Cybersecurity and Infrastructure Security Agency via its official GovDelivery bulletin]
What remains unknown
Evidence limits · The accessible bulletin does not name affected organizations or break its reported minimum down by country or sector. ICU has not independently verified each incident, losses or recovery outcomes. The full technical advisory was unavailable during this review, so this report is limited to the official bulletin. The October 20 release, its retrospective count since August 2024 and this first ICU report are different dates: this source supplies no new October 26 total. It also does not establish that any particular organization is currently compromised. [Cybersecurity and Infrastructure Security Agency via its official GovDelivery bulletin]
Agency-attributed cybersecurity reporting, not a finding that any particular organization is compromised or a guarantee of protection. One joint-advisory origin; individual incidents are not independently verified.
Read the infographic as text
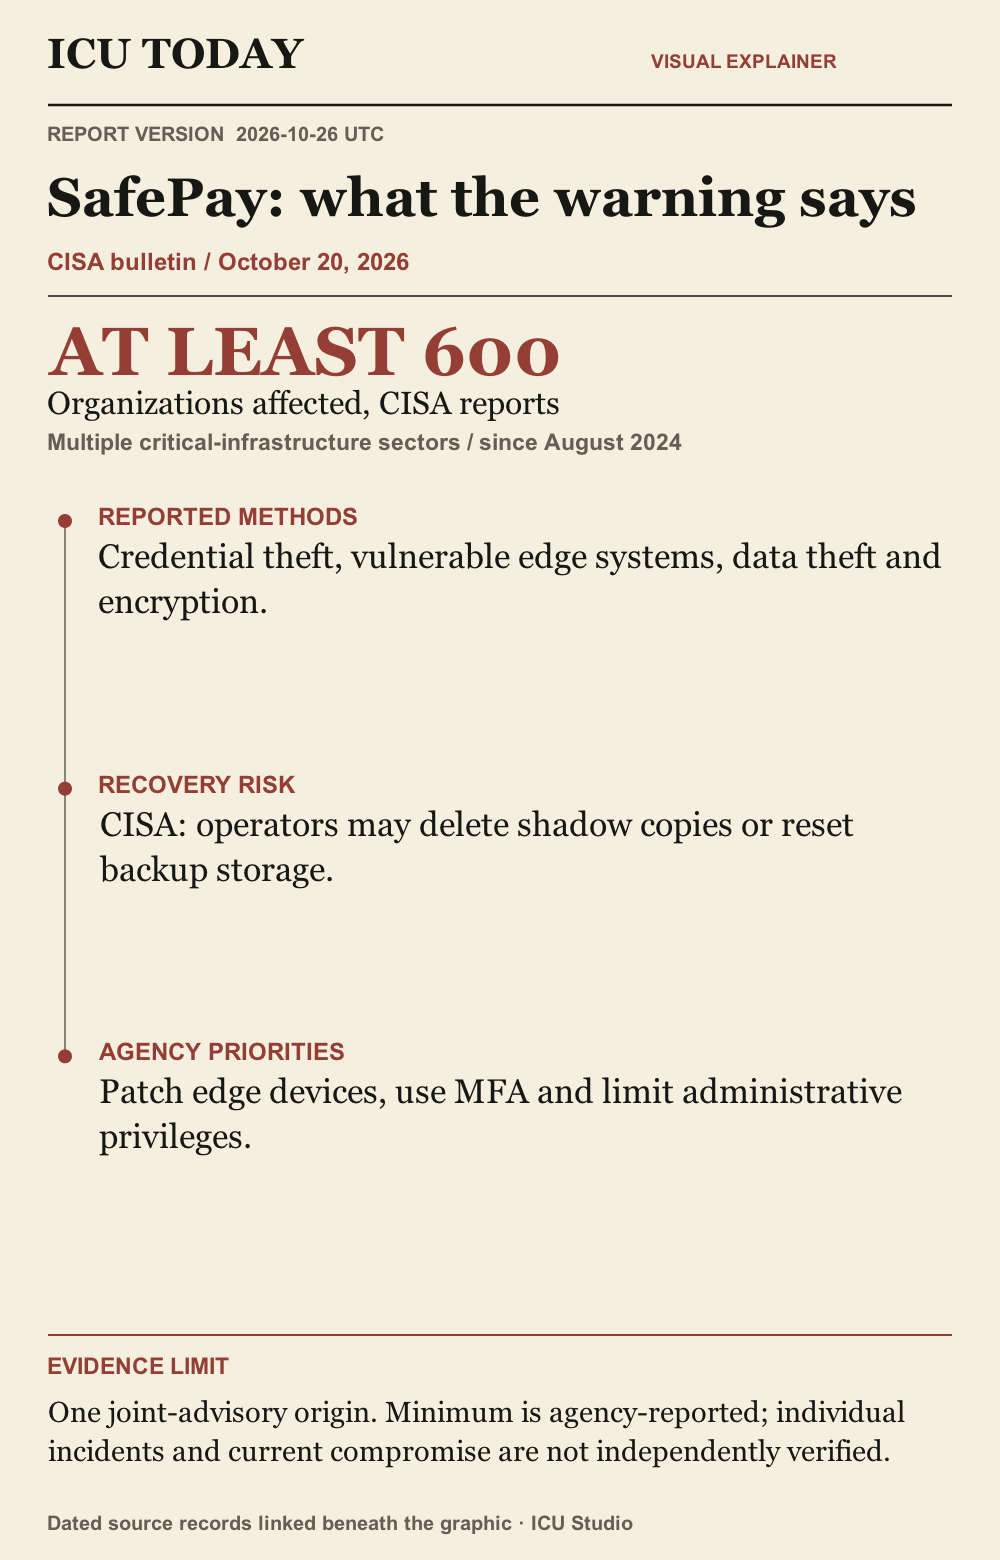
AT LEAST 600. Organizations affected, CISA reports. Multiple critical-infrastructure sectors / since August 2024
REPORTED METHODS. Credential theft, vulnerable edge systems, data theft and encryption.
RECOVERY RISK. CISA: operators may delete shadow copies or reset backup storage.
AGENCY PRIORITIES. Patch edge devices, use MFA and limit administrative privileges.
Evidence limit. One joint-advisory origin. Minimum is agency-reported; individual incidents and current compromise are not independently verified.
Graphic sources: Cybersecurity and Infrastructure Security Agency via its official GovDelivery bulletin
The developing record.
Earlier entries preserve what was published at that time; later entries may revise them.
2026-10-26T12:36:08.621Z · Initial report on the October 20 joint warning, with CISA’s reported minimum since August 2024, attack methods and mitigation priorities. The source provides no new October 26 incident total or independently verified victim count.
SafePay warning: CISA reports at least 600 organizations affected
The October 20 advisory describes ransomware methods and backup disruption. Its reported minimum is not a new October 26 incident tally.
What happened
In an October 20 bulletin, CISA said SafePay ransomware had affected at least 600 organizations across multiple critical-infrastructure sectors since August 2024. It described activity in North and South America, Europe and Australia. The bulletin announced a joint advisory by CISA, the FBI, the U.S. Secret Service and international partners. The agency described exposed credentials, password guessing, VPN access, phished account profiles and vulnerable internet-facing systems as entry routes. It said operators steal data, encrypt systems, threaten disclosure and may delete shadow copies or reset backup storage to disrupt recovery. [Cybersecurity and Infrastructure Security Agency via its official GovDelivery bulletin]
Why it matters
CISA presents the advisory as guidance to reduce both the likelihood and impact of an incident. Its recommended priorities are patching VPNs, firewalls and other edge devices, quickly remediating known-exploited vulnerabilities, strengthening identity and credential controls with multifactor authentication, and restricting administrative tools and privileges to necessary users. These are the agencies’ recommendations; the bulletin does not promise that any one control prevents compromise. Its account covers data theft as well as encryption and backup interference, without establishing that every affected organization experienced every technique. [Cybersecurity and Infrastructure Security Agency via its official GovDelivery bulletin]
What remains unknown
The accessible bulletin does not name affected organizations or break its reported minimum down by country or sector. ICU has not independently verified each incident, losses or recovery outcomes. The full technical advisory was unavailable during this review, so this report is limited to the official bulletin. The October 20 release, its retrospective count since August 2024 and this first ICU report are different dates: this source supplies no new October 26 total. It also does not establish that any particular organization is currently compromised. [Cybersecurity and Infrastructure Security Agency via its official GovDelivery bulletin]
Read the infographic as text
AT LEAST 600. Organizations affected, CISA reports. Multiple critical-infrastructure sectors / since August 2024
REPORTED METHODS. Credential theft, vulnerable edge systems, data theft and encryption.
RECOVERY RISK. CISA: operators may delete shadow copies or reset backup storage.
AGENCY PRIORITIES. Patch edge devices, use MFA and limit administrative privileges.
Evidence limit. One joint-advisory origin. Minimum is agency-reported; individual incidents and current compromise are not independently verified.
Graphic sources: Cybersecurity and Infrastructure Security Agency via its official GovDelivery bulletin
Original sources
CISA joint SafePay advisory bulletin, October 20 · Issuer: CISA, FBI, U.S. Secret Service and international partners · 2026-10-20T19:00:00.000Z
Corrections
No corrections recorded.