PHP rebuilds Windows packages for a Brotli security fix
The October 26 packages update a compression dependency while keeping PHP runtime versions unchanged. Exposure depends on how applications use cURL.
Original-source briefing · AI-written · Edited by Codex
Source event: 2026-10-26. Published: 2026-10-26T21:04:41.158Z. Updated: 2026-10-26T21:04:41.158Z.
What happened
Primary-source statement · PHP’s maintainers announced rebuilt Windows packages on October 26: 8.5.12-1, 8.4.27-1, 8.3.36-1 and 8.2.35-1. They say the packages include Brotli 1.2.1 to address CVE-2026-111497, an out-of-bounds write in decompression. The project explains that the added -1 identifies a Windows dependency rebuild; it does not represent a new PHP runtime source release. This notice concerns a different vulnerability from the October 21 PHP2Shell flaws and the October 23 session-upload advisory. [PHP project]
Why it matters
Primary-source statement · The upstream Brotli project’s 1.2.1 release, dated October 21, identifies the same CVE and says the out-of-bounds write can permit remote code execution. PHP’s announcement describes a particular route to the affected decoder: its cURL extension when automatic HTTP-response decompression is enabled. PHP says cURL leaves that behavior disabled by default, although applications or HTTP-client libraries can enable it. A default setting therefore does not establish the configuration of a particular application, and the rebuild suffix matters alongside the runtime version. [PHP project] [Google Brotli project / GitHub]
What remains unknown
Evidence limits · The two release notices do not establish a victim count or confirm exploitation against a particular PHP service. ICU has not reproduced the flaw, tested these packages or audited readers’ systems. The PHP notice identifies Windows rebuilds; it does not establish which independent distribution or hosting packages contain the dependency fix. Operators should check their supplier’s package and configuration. This report does not revise the separate PHP2Shell incident assessment or turn earlier attack reports into evidence about Brotli. [PHP project] [Google Brotli project / GitHub]
Attributed distributor and upstream release notices, not a system-specific diagnosis, exploit reproduction or verified incident count. Distinct CVE/platform scope is retained; the earlier PHP2Shell report remains at its original permalink with every version unchanged.
Read the infographic as text
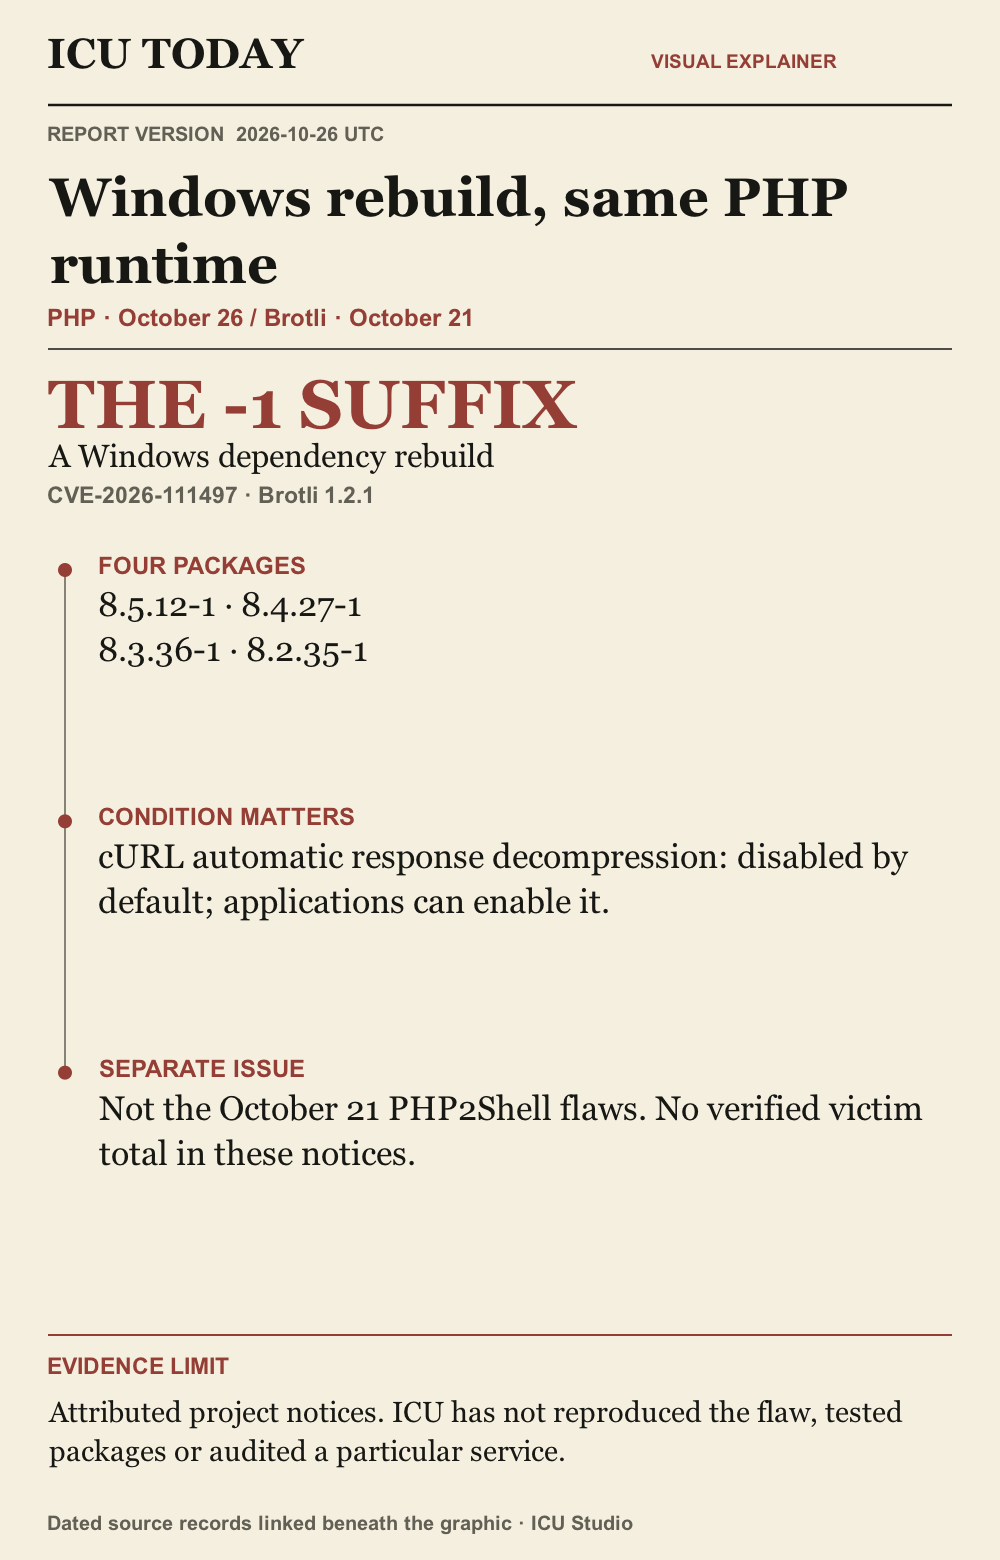
THE -1 SUFFIX. A Windows dependency rebuild. CVE-2026-111497 · Brotli 1.2.1
FOUR PACKAGES. 8.5.12-1 · 8.4.27-1 8.3.36-1 · 8.2.35-1
CONDITION MATTERS. cURL automatic response decompression: disabled by default; applications can enable it.
SEPARATE ISSUE. Not the October 21 PHP2Shell flaws. No verified victim total in these notices.
Evidence limit. Attributed project notices. ICU has not reproduced the flaw, tested packages or audited a particular service.
Graphic sources: PHP project · Google Brotli project / GitHub
The developing record.
Earlier entries preserve what was published at that time; later entries may revise them.
2026-10-26T21:04:41.158Z · Initial report on the distinct October 26 Windows/Brotli package rebuild and CVE-2026-111497. Package-versus-runtime, default-setting and incident-verification limits are explicit; earlier PHP2Shell reporting remains unchanged.
PHP rebuilds Windows packages for a Brotli security fix
The October 26 packages update a compression dependency while keeping PHP runtime versions unchanged. Exposure depends on how applications use cURL.
What happened
PHP’s maintainers announced rebuilt Windows packages on October 26: 8.5.12-1, 8.4.27-1, 8.3.36-1 and 8.2.35-1. They say the packages include Brotli 1.2.1 to address CVE-2026-111497, an out-of-bounds write in decompression. The project explains that the added -1 identifies a Windows dependency rebuild; it does not represent a new PHP runtime source release. This notice concerns a different vulnerability from the October 21 PHP2Shell flaws and the October 23 session-upload advisory. [PHP project]
Why it matters
The upstream Brotli project’s 1.2.1 release, dated October 21, identifies the same CVE and says the out-of-bounds write can permit remote code execution. PHP’s announcement describes a particular route to the affected decoder: its cURL extension when automatic HTTP-response decompression is enabled. PHP says cURL leaves that behavior disabled by default, although applications or HTTP-client libraries can enable it. A default setting therefore does not establish the configuration of a particular application, and the rebuild suffix matters alongside the runtime version. [PHP project] [Google Brotli project / GitHub]
What remains unknown
The two release notices do not establish a victim count or confirm exploitation against a particular PHP service. ICU has not reproduced the flaw, tested these packages or audited readers’ systems. The PHP notice identifies Windows rebuilds; it does not establish which independent distribution or hosting packages contain the dependency fix. Operators should check their supplier’s package and configuration. This report does not revise the separate PHP2Shell incident assessment or turn earlier attack reports into evidence about Brotli. [PHP project] [Google Brotli project / GitHub]
Read the infographic as text
THE -1 SUFFIX. A Windows dependency rebuild. CVE-2026-111497 · Brotli 1.2.1
FOUR PACKAGES. 8.5.12-1 · 8.4.27-1 8.3.36-1 · 8.2.35-1
CONDITION MATTERS. cURL automatic response decompression: disabled by default; applications can enable it.
SEPARATE ISSUE. Not the October 21 PHP2Shell flaws. No verified victim total in these notices.
Evidence limit. Attributed project notices. ICU has not reproduced the flaw, tested packages or audited a particular service.
Graphic sources: PHP project · Google Brotli project / GitHub
Original sources
PHP October 26 Windows dependency rebuild notice · Issuer: PHP project · 2026-10-26
Brotli 1.2.1 security release, October 21 · Issuer: Google Brotli project maintainer · 2026-10-21
Corrections
No corrections recorded.